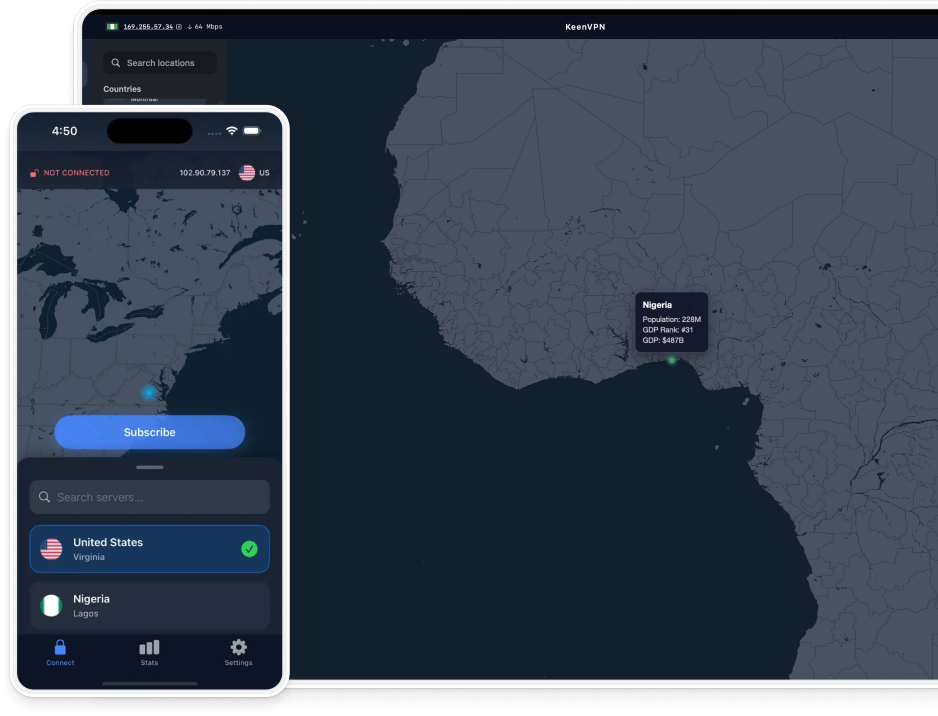
KeenVPN privacy policy explained is the roadmap to how your data is handled when you use the service. In plain English, this guide walks you through the key clauses, what they mean for you, and why they matter.
TL;DR
- KeenVPN does not store browsing history or destination IPs.
- Only temporary connection logs are kept for troubleshooting, then deleted.
- The policy applies worldwide and respects local legal requests.
- You can verify claims through independent audits and transparency reports.
Why Understanding a VPN Privacy Policy Matters
Most people assume that any VPN automatically guarantees anonymity. The uncomfortable truth is that many providers keep extensive logs that can be handed over to authorities. When you know exactly what a provider does with your data, you can make an informed choice and avoid a false sense of security.
And if you’re streaming, traveling, or working remotely, the stakes are higher. A vague policy can expose you to data breaches or unwanted tracking. So reading the fine print isn’t optional, it’s essential.
KeenVPN Privacy Policy Explained
Visit KeenVPN to view the full document, but here’s the distilled version.
What the Policy Covers: Core Sections
Each bullet in the Quick Answer isn’t just a headline—it represents a concrete practice that shapes how your online footprint is treated. Below we unpack those points, giving you a clearer picture of what “no browsing history” actually looks like on the backend, how “temporary connection logs” are managed, what “global applicability” entails, and why independent verification matters.
Browsing History and Destination IPs Are Not Stored
KeenVPN’s architecture is built around a strict “no‑logs” philosophy for user traffic. When you initiate a tunnel, the service encrypts your packets and forwards them to the exit node without attaching any identifying metadata. The system discards packet headers that could reveal the sites you visit or the IP addresses you connect to. This approach differs from providers that retain detailed session records, which can later be subpoenaed. By not persisting this data, KeenVPN reduces the attack surface for both external hackers and internal misuse, ensuring that even a compromised server cannot retroactively reconstruct your browsing patterns.
Only Temporary Connection Logs Are Kept for Troubleshooting, Then Deleted
Technical logs—such as timestamps of when a connection was established, the amount of data transferred, and the server that handled the request—are retained for a brief window, typically no longer than 24 hours. These logs are essential for diagnosing connectivity issues, detecting abnormal traffic spikes, and maintaining service quality. After the retention period expires, the logs are automatically purged from both volatile memory and persistent storage, leaving no trace that could be linked back to an individual user. This short‑lived logging strikes a balance between operational transparency and privacy preservation.
The Policy Applies Worldwide and Respects Local Legal Requests
KeenVPN operates a network of servers across multiple jurisdictions, but the privacy commitments outlined in the policy are uniformly enforced regardless of where a user connects. When a legal authority issues a request for user data, the provider first verifies the request’s legitimacy under the applicable law. Because the core data (browsing history, destination IPs) simply does not exist in the system, there is nothing to hand over. In the rare cases where connection‑level logs are still within the retention window, KeenVPN evaluates the request against its internal data‑minimization standards before any disclosure, often resulting in either a partial compliance or a full refusal if the request exceeds what is legally permissible.
Independent Audits and Transparency Reports Verify Claims
To substantiate its privacy promises, KeenVPN commissions third‑party security firms to audit its infrastructure and data‑handling practices. The findings are compiled into publicly available transparency reports that detail the number of government requests received, the nature of those requests, and the provider’s response. While the exact audit methodology is proprietary, the reports typically include summaries of the scope, the audit timeline, and any remedial actions taken. This external validation helps users trust that the stated policies are not merely marketing language but are backed by measurable, repeatable processes.
References
- Virtual private network - Wikipedia -- General definition of VPN and privacy concepts
- Electronic Frontier Foundation. Surveillance and Privacy -- Authoritative source on privacy rights and data collection
- U.S. Federal Trade Commission. Data Security -- Guidelines on data protection and consumer privacy
.png)
No comments yet. Be the first to share your thoughts!
Leave a Comment